

Website security can seem complicated, especially if you’re a business owner rather than a developer.
The good news is that you don’t need to understand every technical detail to understand the most common risks.
Knowing where problems can occur can help you make better decisions about website development and maintenance.
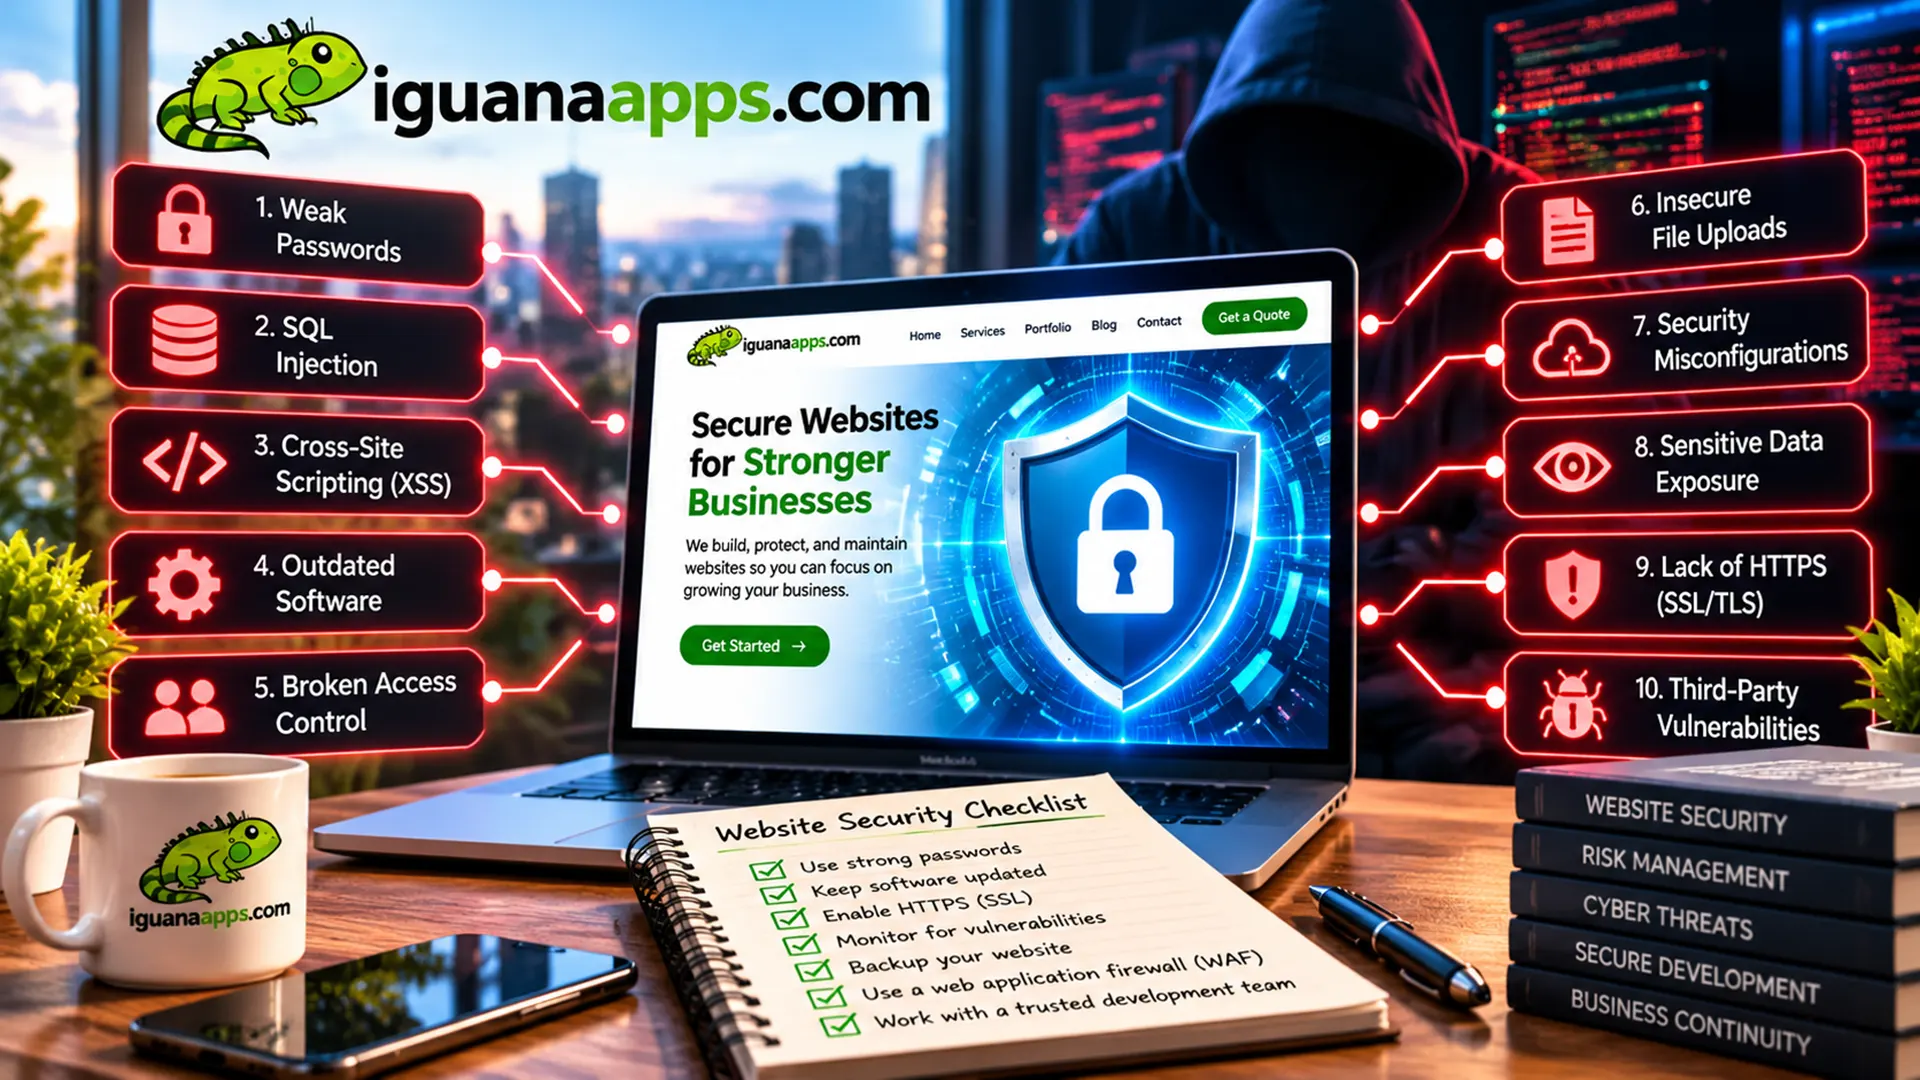
Here are ten common security areas businesses should understand.
- Weak Passwords
Weak or reused passwords can make accounts easier to compromise.
Administrative accounts should use strong, unique credentials.
Where available, multi-factor authentication can provide another layer of protection.
- Outdated Software
Websites often depend on multiple software components.
If those components aren’t maintained, known security problems may remain unresolved.
Regular updates should be part of website maintenance.
- Excessive User Permissions
Giving every user administrator-level access creates unnecessary risk.
Instead, users should generally receive only the permissions they need to perform their responsibilities.
- Poorly Secured Forms
Contact forms, registration forms, and other input fields should be designed with security in mind.
Applications should properly validate and handle information submitted by users.
- Insecure File Uploads
Some websites allow users or administrators to upload files.
If file uploads aren’t properly controlled, they can create security risks.
Developers should carefully restrict what can be uploaded and how uploaded files are handled.
- Unprotected Administrative Areas
Website administration systems should not be treated like ordinary public pages.
Businesses should use appropriate authentication, permissions, and security controls.
- Insecure Third-Party Integrations
Modern websites often connect to external services.
Examples include:
- Payment systems
- Marketing platforms
- CRMs
- Analytics
- Shipping systems
- Social platforms
Each integration should be evaluated carefully.
- Missing Backups
A business may discover the importance of backups only after something goes wrong.
Regular backups provide an important recovery mechanism.
Backups should be stored appropriately and tested periodically.
- Poor Hosting Configuration
Website security isn’t limited to the application itself.
Hosting and server configuration can also affect security.
Businesses should work with qualified professionals or reputable hosting providers to ensure their environments are appropriately configured.
- Ignoring Security Updates
Security isn’t a “set it and forget it” task.
A website that was properly configured several years ago may still need updates and maintenance today.
Regular reviews help identify changes that need attention.
Security Is a System
It’s tempting to look for one security product that will solve everything.
Unfortunately, website security doesn’t work that way.
A secure website depends on multiple layers working together.
These can include:
- Secure development
- Strong authentication
- Updates
- Access controls
- Monitoring
- Backups
- Secure hosting
- Proper configuration
Don’t Wait for a Problem
One of the best times to review your website security is before an incident happens.
Ask yourself:
- Who has access to the website?
- Are all accounts still necessary?
- Is the software current?
- Are backups working?
- Is HTTPS configured?
- Are old plugins or integrations still needed?
- When was the last security review?
If you don’t know the answers, it may be time for a professional review.
Need a Website Security Review?
Iguana Technologies can help businesses identify website maintenance and security issues before they become larger problems.
Contact us at Iguana Technologies to discuss your website’s security and maintenance needs.
Contact us
Get a FREE, NO OBLIGATION consultation appointment any time, by filling out the form below!
